Remote Copying Tools, Archiving Tools, Backup & User Management
Day-2 : Linux Workshop
Student, COEP'27 | DBATU'24 | Member of CSI COEP | Full Stack Developer | DSA Enthusiast | Explorer |
These are the topics that are covered in today's session.
Remote Copying Tools:
1 . SCP :
SCP stands for secure copy command in Linux.
It is used to copy the files between the servers securely.
It allows the secure transfer of files between the local host and the remote host or between two remote hosts.
#Syntax :
scp <filename> <remoteuser>@<remoteuserIP>:<destination>
#Example:
scp myLinuxFile root@192.168.100.7:/root
2 . RSYNC:
RSYNC stands for remote synchronisation command in Linux.
It synchronizes files from a source to a destination.
It is famous for its delta-transfer algorithm, which reduces the amount of data sent over the network by sending only the differences between the source files and the existing files in the destination.
RSYNC finds files that need to be transferred using a checksum algorithm that looks for files that have changed in size or in the last-modified time.
#Syntax:
rsync -av <filename> <remoteuser>@<remoteuserIP>:<destination>
#Example:
rsync -av myLinuxFile root@192.168.100.7:/root
3 . SFTP:
SFTP stands for Safe File Transfer Protocol.
It is a secure variant of FTP.
It is a part of the SSH Protocol and is designed to securely transfer files between remote systems via a network connection.
#Syntax:
sftp <username>@<userIP>
#Example:
sftp linuxUser@192.168.100.7
Archiving Tools:
Archiving is the process of combining multiple files into a single package called an archive.
This archive can then be easily backed up, or simply kept on your machine as a way to organize your file system.
1 . gzip
#Syntax : (Compress)
gzip <filename>

#Example :
gzip myFile
#Syntax : (Decompress)
gunzip <filename>.gz

#Example :
gunzip myFile.gz
2 . xz
#Syntax: (Compress)
xz <filename>

#Example:
xz myFile
#Syntax: (Decompress)
unxz <filename>.xz

#Example:
unxz myFile.xz
3 . bzip2
#Syntax: (Compress)
bzip2 <filename>

#Example:
bzip2 myFile
#Syntax: (Decompress)
bzip2 <filename>.bz2

#Example:
bzip2 myFile.bz2
Backup:
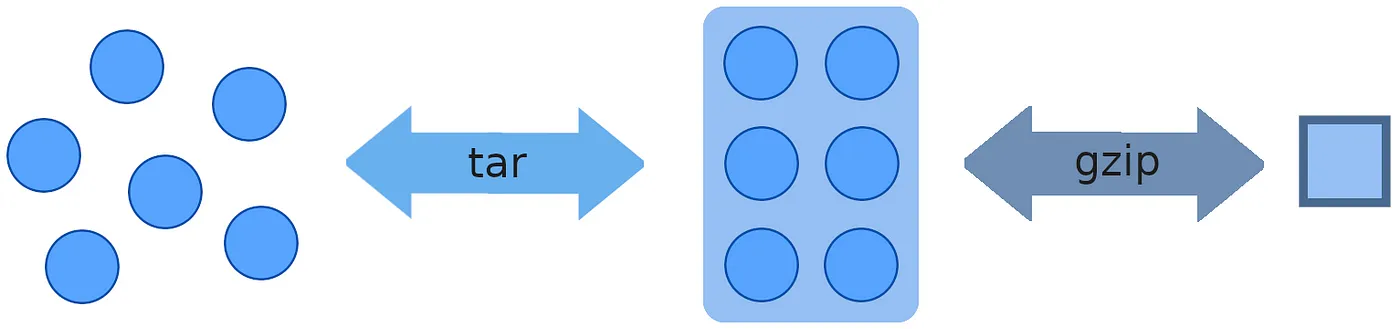
Fig. Regular files being added to an archive with tar and then compressed with gzip.
The tar utility is also able to compress an archive via a compression tool.
To create an archive file :
#Syntax:
tar -cvzf <destn.backup> <sourcefile>

#Example:
tar -cvzf myLinuxFile.backup file1 file2 file3
- To extract an archive file:
#Syntax:
tar -xvf <destn.backup>

#Example:
tar -xvf myLinuxFile.backup
User Management:
A user is an entity, that can manipulate files and perform several other operations.
Each user is assigned an ID that is unique for each user in the operating system.
The ID 0 is assigned to the root user and the IDs 1 to 999 are assigned to the system users, hence the ids for the local user begin from 1000 onwards.
1 . Adding the User :
The command "useradd" or "adduser" can be used to create a new user in Linux also, the sudo permissions are required to perform this command.
  #Creating a User:
  root@myLinux:~# useradd testuser
  #OR
  root@myLinux:~# adduser testuser
2 . Verifying the User:
root@myLinux:~# id testuser
uid=1001(testuser) gid=1001(testuser) groups=1001(testuser)
3 . Deleting the User:
root@myLinux:~# userdel testuser
4 . Managing the password policy:
Fields of /etc/password file:
#The sudo permissions are required to perform this command
root@myLinux:~# cat /etc/passwd|tail -1
testuser:x:1001:1001::/home/testuser:/bin/sh
Where,
testuser --> Name of user
x --> Encrpyted password
1001 --> User id
1001 --> Group id
:: --> Nickname (Con-name)
/home/testuser --> Home directory of the user
/bin/bash --> Default shell of user
Setting the password :
#The sudo permissions are required to perform this command
root@myLinux:~# passwd testuser
#Next...
New password: 123
Retype new password: 123
passwd: password updated successfully
Changing the password policy:
root@myLinux:~# chage -M 2 -m 5000 -W 4 -I 12 -E 2024-12-2
Where,
-M --> maxdays password change date
-m --> mindays password change date
-W --> warning
-I --> Inactivity
-E --> Account Expiry date
5 . Change / Restrict the User:
Give "No Login" to the User:
root@myLinux:~# usermod testuser -s /sbin/nologin

#Verifying...
root@myLinux:~# su - testuser
Cannot change directory to /home/testuser:
No such file or directory
This account is currently not available.
To revert the changes to get a login:
root@myLinux:~# usermod testuser -s /bin/sh

#Verifying...
root@myLinux:~# su - testuser
Last Login : .....
$whoami
testuser
6 . Lock and Unlock User:
# To Lock the user:
root@myLinux:~# usermod -L testuser

# To Unlock the user:
root@myLinux:~# usermod -U testuser
7 . Adding Group:
#The sudo permissions are required to perform this command
root@myLinux:~# groupadd testgroup

#Verifying the group...
root@myLinux:~# cat /etc/group|tail -1
testgroup:x:1002:
8 . Adding a user to a group:
root@myLinux:~# usermod -G testgroup testuser

#Verifying...
root@myLinux:~# id testuser
uid=1001(testuser) gid=1001(testuser) groups=1001(testuser),1002(testgroup)
9 . Deleting a group:
root@myLinux:~# groupdel testgroup

#Verifying...
root@myLinux:~# id testuser
uid=1001(testuser) gid=1001(testuser) groups=1001(testuser)
10 . Change the user-id of the user:
root@myLinux:~# usermod -u 1005 testuser

#Verifying...
root@myLinux:~# id testuser
uid=1005(testuser) gid=1001(testuser) groups=1001(testuser)